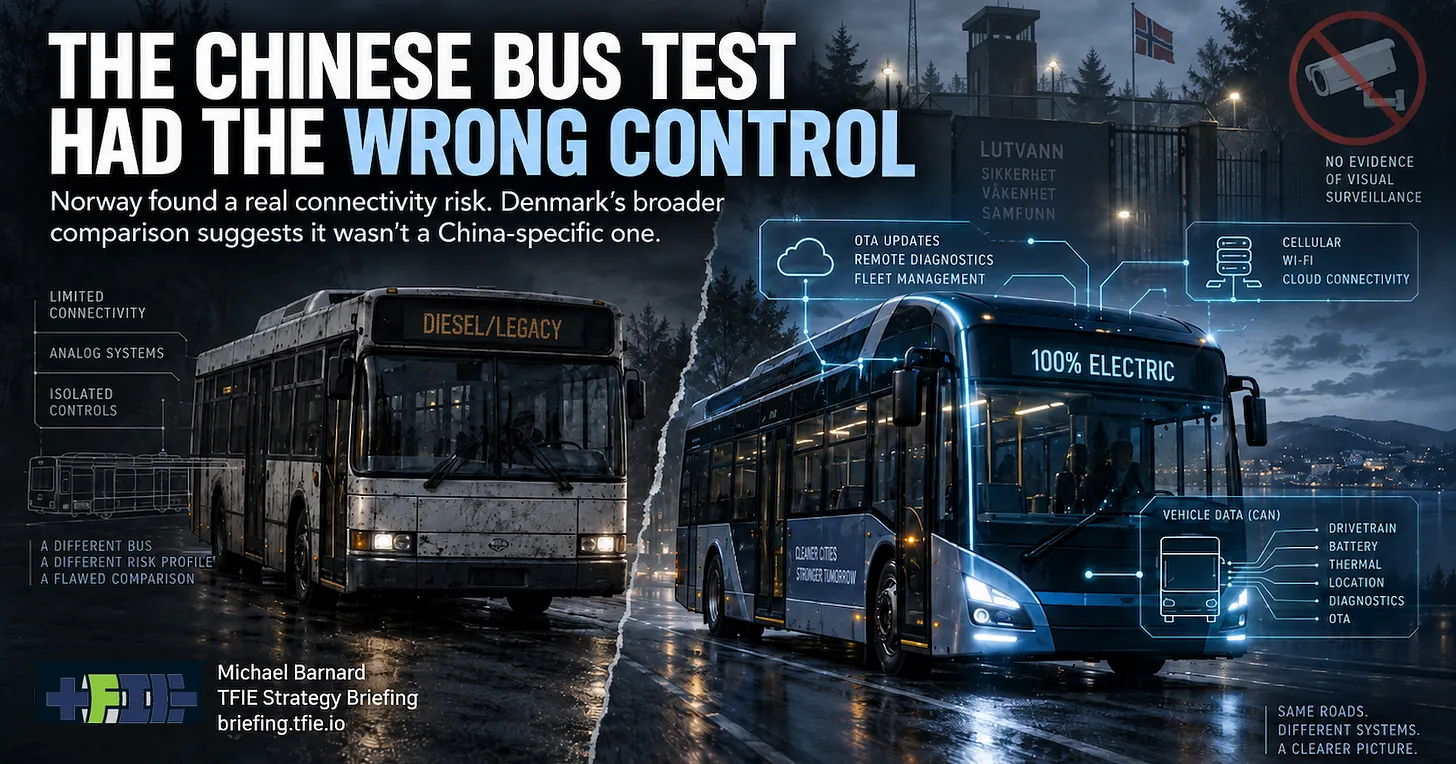
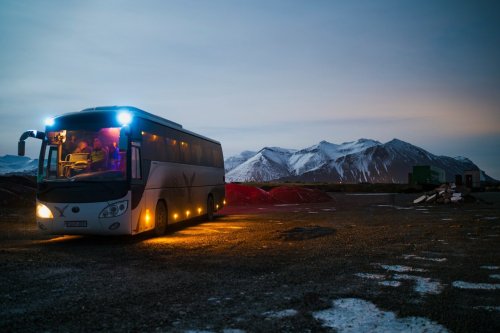
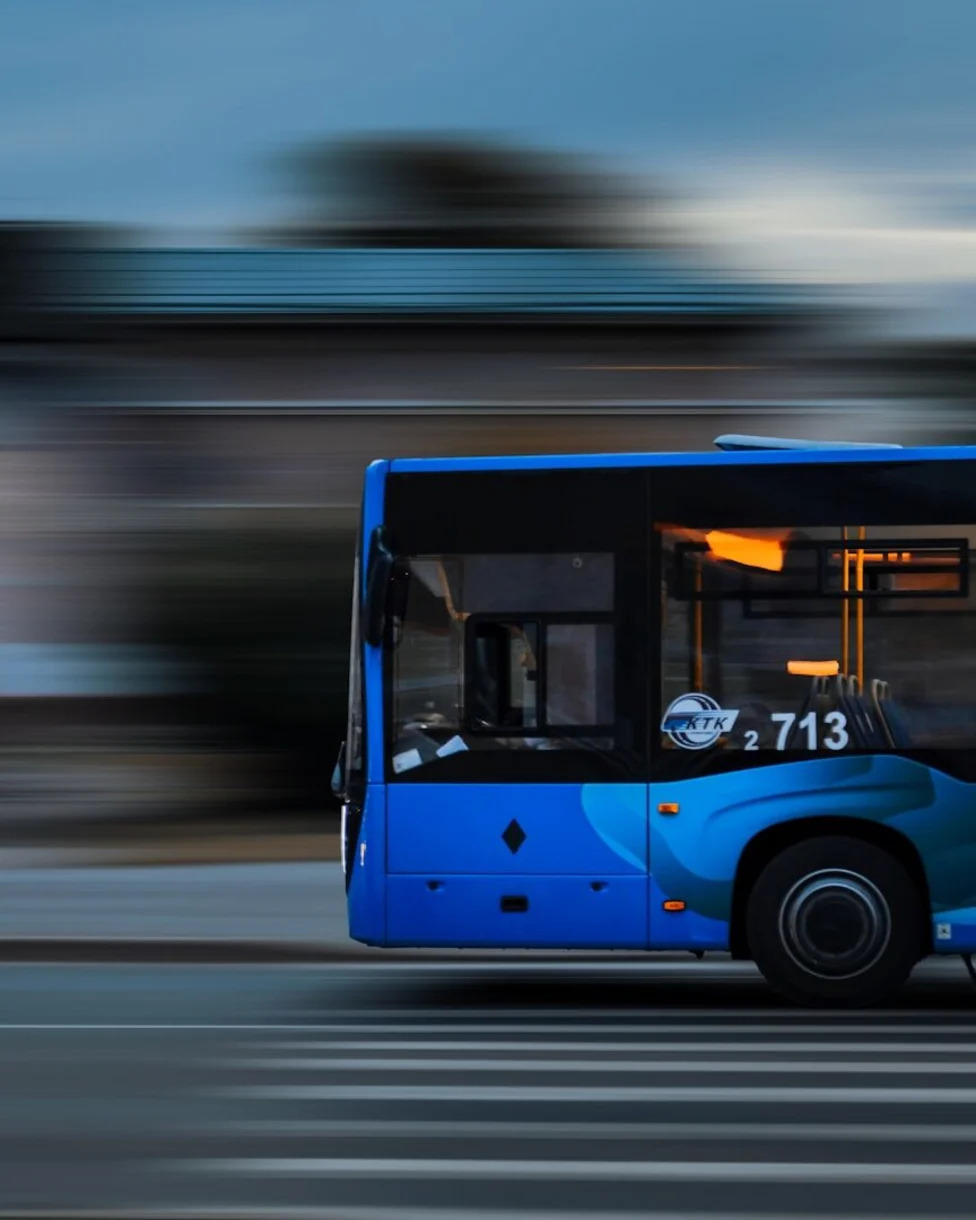
When Norwegian transit authority Ruter put a Chinese Yutong electric bus through cybersecurity testing inside an isolated mine, the investigation started with two very different concerns. One was geopolitical: could the bus act as a visual-surveillance platform near sensitive facilities such as Lutvann, home to Norway’s intelligence service? The other was technological: could a manufacturer with remote diagnostics and over-the-air software access reach systems important enough to interfere with the bus? Those questions travelled together in the public discussion, but they were technically distinct and ultimately produced very different answers. The full TFIE Strategy Briefing analysis asks what the Norwegian experiment actually isolated, and whether its choice of control could distinguish a Chinese security problem from the ordinary risks of modern connected vehicles. The explicitly espionage-focused hypothesis produced the less dramatic result. Investigators found that the Yutong’s exterior camera system was isolated from the manufacturer’s online systems, while the interior surveillance system used operator-side connectivity rather than a covert path back to Yutong. The concern that the bus could function as a rolling visual-surveillance platform around Lutvann was not supported. The remote-access question did produce a real finding: Ruter identified an internet-connected path through the manufacturer’s systems into operationally important parts of the vehicle. With sufficient privilege, that access could potentially interfere with operation and render the bus unusable. The security issue was real; what remained unresolved was whether it had anything to do with the bus being Chinese. Ruter compared the 2025 Yutong with a 2022 VDL whose critical systems had little external connectivity and which could not autonomously receive over-the-air updates. Manufacturer, country of origin, vehicle age, connectivity, OTA capability and electronic architecture all changed at once. The experiment showed that a highly connected bus could be reached remotely while a comparatively disconnected one could not, but that pairing could not isolate nationality as the reason. If the objective was simply to establish whether that particular Yutong had consequential remote access, the test was useful. If the evidence was going to inform claims about Chinese buses presenting a distinctive remote-control risk, a contemporary connected European bus would have been far more revealing. Ruter had such buses available. Its network included newer European electric buses from MAN and Solaris, both manufacturers with mature digital architectures supporting remote diagnostics, backend communications and software-related functions. Putting the Yutong beside one of them would have allowed investigators to ask the same questions under comparable conditions: what could the manufacturer reach, what could it change, how were updates authenticated, how well were propulsion and battery systems segmented, what activity was logged, and could the operator independently sever outside access? The result might have exposed a Yutong-specific weakness, shown that European buses behaved similarly, or identified meaningful differences among manufacturers. Instead, the European control largely lacked the technology at the centre of the investigation. As the Norwegian findings travelled, the negative Lutvann result received much less attention than the successful remote-access finding, which was often translated into a story about Chinese buses containing a remote “kill switch.” That compressed two different findings into a much simpler geopolitical narrative. There is nothing unreasonable about transit agencies testing hostile-state scenarios, particularly when suppliers retain remote access to public infrastructure, but country-specific concerns demand good controls. Comparing a highly connected Chinese vehicle with a comparatively disconnected European one makes it easy to attribute a technological difference to nationality even though the experiment itself does not support that step. Denmark later approached the issue from another direction. Movia commissioned EY to assess cybersecurity maturity across Chinese and European bus manufacturers using the same automotive cybersecurity frameworks. The work was not a penetration test and therefore cannot substitute for Ruter’s hands-on examination, but it did make the cross-manufacturer comparison that the Norwegian public debate implied had already been settled. Chinese manufacturers did not emerge as cybersecurity laggards, and Movia concluded there was no basis for considering Chinese buses less cybersecure than buses from other manufacturers. That finding does not establish that every Yutong implementation is equivalent to every European one. It does make nationality a much weaker explanation for what Ruter discovered. Taken together, the Norwegian and Danish work point to a more useful security problem. Modern buses are networked computers, and transit agencies need to know who can remotely reach them, which systems are exposed, what software can be changed, how updates are authenticated, what activity is logged and how quickly outside access can be severed if a supplier is compromised or becomes hostile. Those requirements belong in procurement and fleet management whether the badge says Yutong, MAN, BYD, Solaris, Mercedes-Benz or Volvo. Norway found a good reason to investigate remote bus access. Its choice of control simply could not tell it whether China was the reason the access existed. Read the full analysis on TFIE Strategy Briefing.